The Agentic AI Roadmap: From One Workflow to a Managed Agent Program

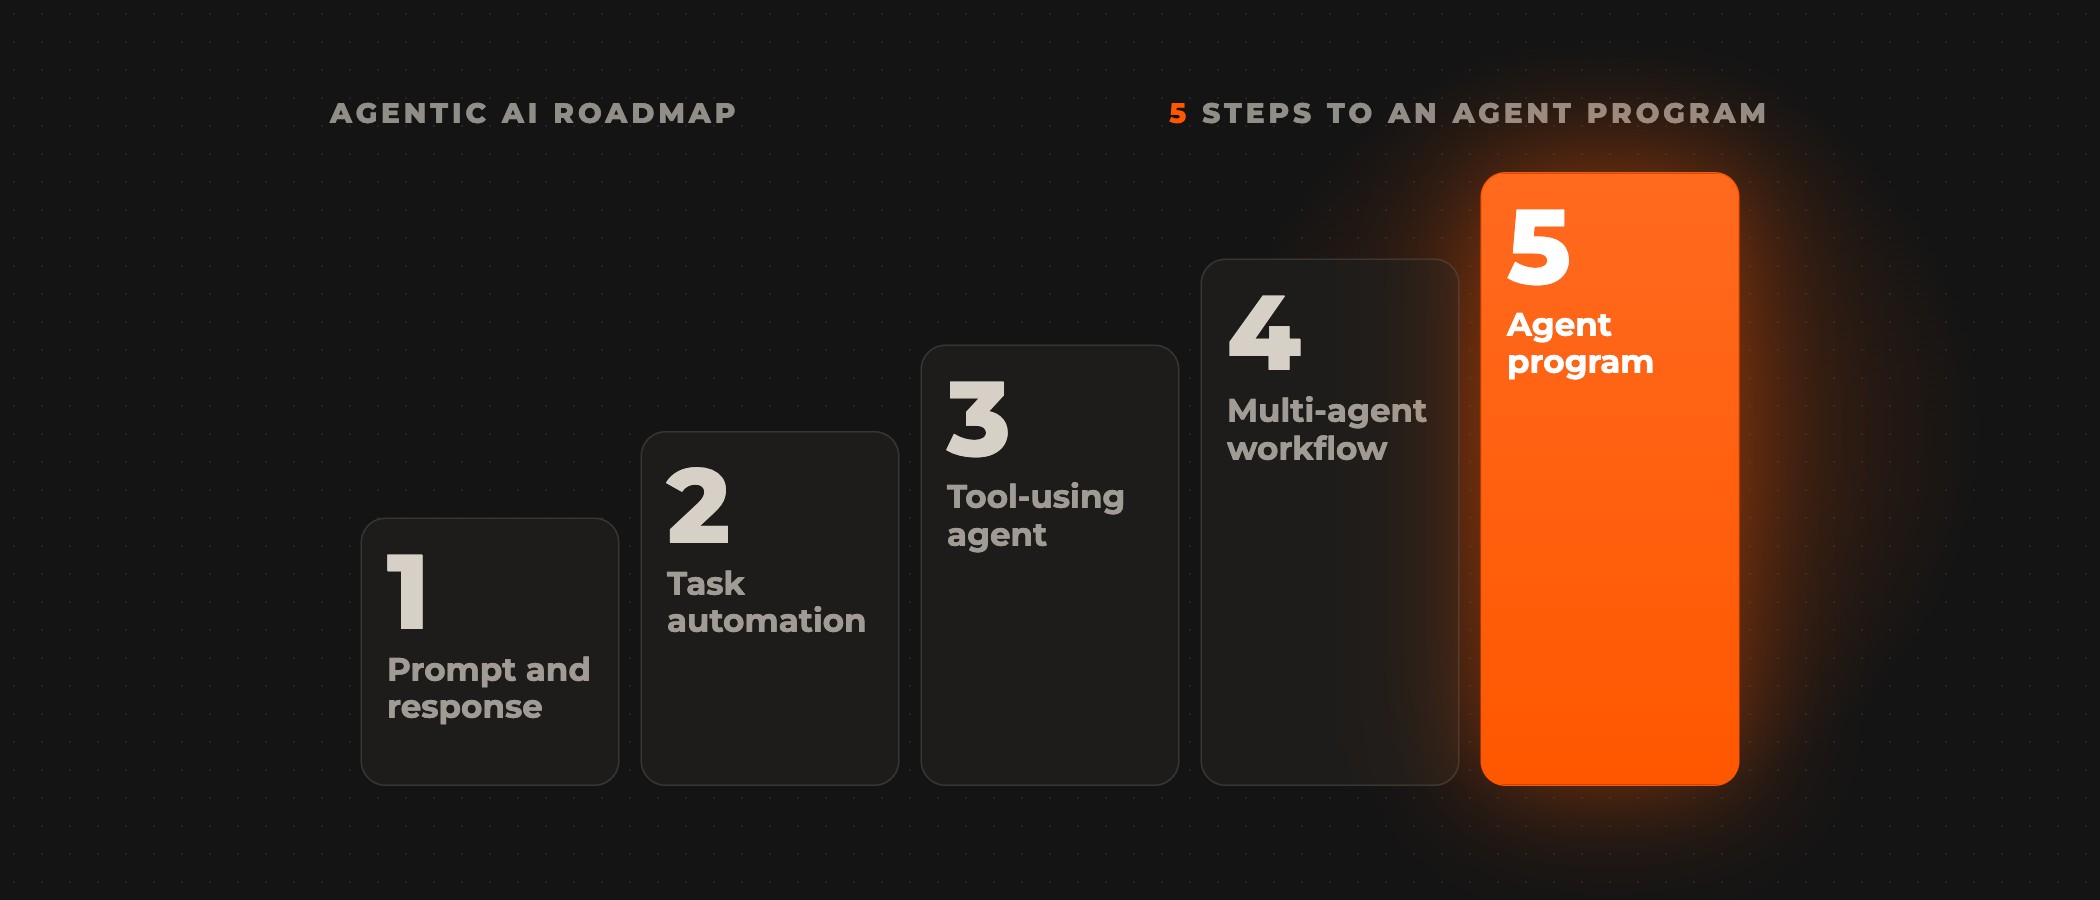
An agentic AI roadmap takes one AI workflow in production and grows it into a managed program of agents. You add four things in order. First comes shared orchestration, one system that runs and monitors every agent. Then come open connections to your tools and governance matched to what each agent may do. Last comes an operating rhythm, meaning a set routine for running and reviewing agents, with an owner for every agent. The order matters because each new agent is built on whatever the first one was built on.
Skipping that order is expensive. Gartner predicted in June 2025 that over 40% of agentic AI projects will be canceled by the end of 2027. The causes it named are escalating costs, unclear business value or inadequate risk controls. McKinsey's State of AI in 2026 looked at companies with more than $1 billion in revenue. There, 40% of respondents now report scaling AI agents, up from 27% a year earlier. At smaller companies the figure stayed flat at 22%.
What is an agentic AI roadmap?
An agentic AI roadmap is the plan for moving from single AI tasks to agents. Those agents plan, use tools and hand work to each other inside your systems. It covers three tracks at once: the architecture the agents run on, the governance rules on what each agent may do, and the people who own and review the work.
In the same June 2025 release, Gartner predicted that by 2028, AI agents will make at least 15% of day-to-day work decisions on their own. In 2024, that share was zero. Gartner also predicted that 33% of enterprise software applications will include agentic AI by then, up from under 1%. That means many of the agents your teams meet will arrive inside software you already buy. Your roadmap has to cover those agents as well as the ones you build.
It sits one level below an enterprise AI strategy, which sets the goals AI serves. Our AI adoption framework covers where a company stands across all its AI work. This roadmap is for the team that has one agent working and is asked for ten more.
The five steps from one workflow to an agent program
Each step adds one capability, and each capability needs something in place before it ships.
| Step | What the AI does | Add before it ships | Who checks it |
|---|---|---|---|
| 1. Prompt and response | Answers a question when asked | Rules on which data may go into prompts | The person who asked |
| 2. Task automation | Runs one fixed task inside a workflow | Failure alerts and a baseline | The workflow owner |
| 3. Tool-using agent | Decides which tool to call and when | Scoped tool access and run logs | A checking agent, then a person |
| 4. Multi-agent workflow | Hands work between specialised agents | Shared orchestration and state | Approval steps on actions that write |
| 5. Agent program | Runs many agents across teams | A register, owners and autonomy levels | Governance, on a fixed review cycle |
Start with one workflow that earns the next
The first agent should be useful on its own and teach you what the program will need. Pinkcube's chat desk was staffed 45 hours a week. The agent we built answers in Dutch or English around the clock. It checks live order status, and when it cannot help, a sorted HubSpot ticket is filed. A second agent, the Gatekeeper, checks every reply before the customer sees it. Before launch the agent faced 76 hostile test scenarios, and 64 scored 5 out of 5, as the Pinkcube case sets out.
That one workflow already holds the parts of a program: three agents with separate jobs, permissions split between them, and a set of tests run before go-live. The chat agent has no permission to create tickets. A separate triage agent decides whether a person must follow up. We now run twelve production systems for Pinkcube.
What architecture does a multi-agent system need?
A multi-agent system needs five layers, and most pilots skip the orchestration layer. Without it, each agent runs as its own script with its own retries, logs and credentials, and nobody can see the program as a whole.
- Orchestration. One engine passes work between agents, tracks where each task stands, retries failures and alerts the owner. We use self-hosted n8n in queue mode. A main instance hands each run to a Redis queue and separate workers carry it out, so you handle more volume by adding workers.
- Models chosen per task. For each article, GoKickflip's content pipeline runs about 33 agent executions across six or more models. It picks the model for each step instead of using one model for everything, as the GoKickflip case shows.
- Open tool connections. The Model Context Protocol (MCP) gives agents one standard way to reach your tools and data. In December 2025, Anthropic donated MCP to the Agentic AI Foundation, a fund under the Linux Foundation, so no single vendor controls it.
- Guardrails. Fixed rules the model cannot override, a checking agent that reviews output before it reaches people, and approval steps on actions that write data.
- Shared context. An enterprise context layer lets every agent read the same company data, with access rules checked before anything is read.
Buying ready-made agents does not remove these layers. Gartner estimates that only about 130 of the thousands of vendors selling agentic AI offer real agents. It calls the rest agent washing, meaning chatbots and robotic process automation tools that have been relabelled. If you would rather hire a firm to build the agents, our list of the top AI consulting companies for enterprise in 2026 shows which kind of firm fits which job.
How should AI agent governance grow with autonomy?
Govern each agent by what it is allowed to do, instead of applying one policy to all of them. Gartner warned in May 2026 that by 2027, 40% of enterprises will demote or decommission autonomous AI agents because of governance gaps found only after production incidents. It set out four levels, each with its own controls. Pick a level below to see what it requires.
An agent moves up a level when its logs show it handles the work at the level below. That keeps the register accurate, because every agent has an owner, a level and the evidence that put it there. Our AI governance framework sets the levels, approval steps and escalation paths before the first agent goes live. The business unit adoption guide covers who owns each workflow inside the unit.
How to run an agent program once it is live
- Keep a register. List every agent with its owner, its autonomy level, the tools it can call and the data it can read.
- Put failures in front of the builder. A failed run should pause the workflow, hold the records and alert the engineer who built it. That way nothing bad gets written while the fix is made.
- Ship changes through staging. Test every prompt, model and tool change in a pre-production copy before it goes live. Then rerun the records that were held back.
- Watch cost per run. McKinsey found about one in five respondents say the cost of running AI now limits how much they use it. That includes token costs, the usage fees AI model providers charge. The AI agent cost estimator prices one run of your agent on nine Claude, GPT and Gemini models.
- Review autonomy on a fixed cycle. Raise or lower each agent's level on what its logs show since the last review.
Our AI managed services run this loop every week on each workflow we operate. We ship changes, watch the runs, catch failures, fix them and report what each workflow saved.
Frequently asked questions
What is an agentic AI roadmap?
It is the plan for growing one AI workflow in production into a program of agents. It sets the order in which you add orchestration, tool connections, governance by autonomy level and an operating rhythm, with an owner for every agent.
What are the components of a multi-agent system?
There are five. Orchestration routes work and tracks each task, and models are chosen per task. Tool connections include MCP servers and APIs. Guardrails include checking agents and approval steps, and shared context comes with access rules. Run logs and an agent register cover all five.
How do you govern AI agents?
Match the controls to what each agent may do. Gartner describes four levels, from read-only agents to agents that act on their own within guardrails. Each level adds controls, such as testing for made-up answers (hallucinations), approval workflows with audit trails, or automatic shut-offs (circuit breakers) and rollback.
How long does it take to build an agentic AI program?
It depends on how many systems each agent touches. As a guide, our guarded chat agent builds go from kickoff to live in 5 to 7 weeks. The AI Audit, which produces a ranked 90-day roadmap, takes 4 to 8 weeks.
Do we need to clean all our data before building agents?
No. Start with the data the first workflow needs, connect it through access rules and fix gaps as the workflow exposes them. The AI Audit puts a cost on the data gaps for each use case before a build is approved.
If you have one agent working and need the plan for the next ten, book a discovery call. A senior partner will ask what is running today. The enterprise AI roadmap from the AI Audit then turns the answer into a ranked 90-day plan, with an owner on every item.


